Network design for mid-size companies: segmentation, redundancy and zero trust
A good network design stops one compromised laptop from reaching everything, and keeps the business running when a link fails. Neither needs exotic equipment.
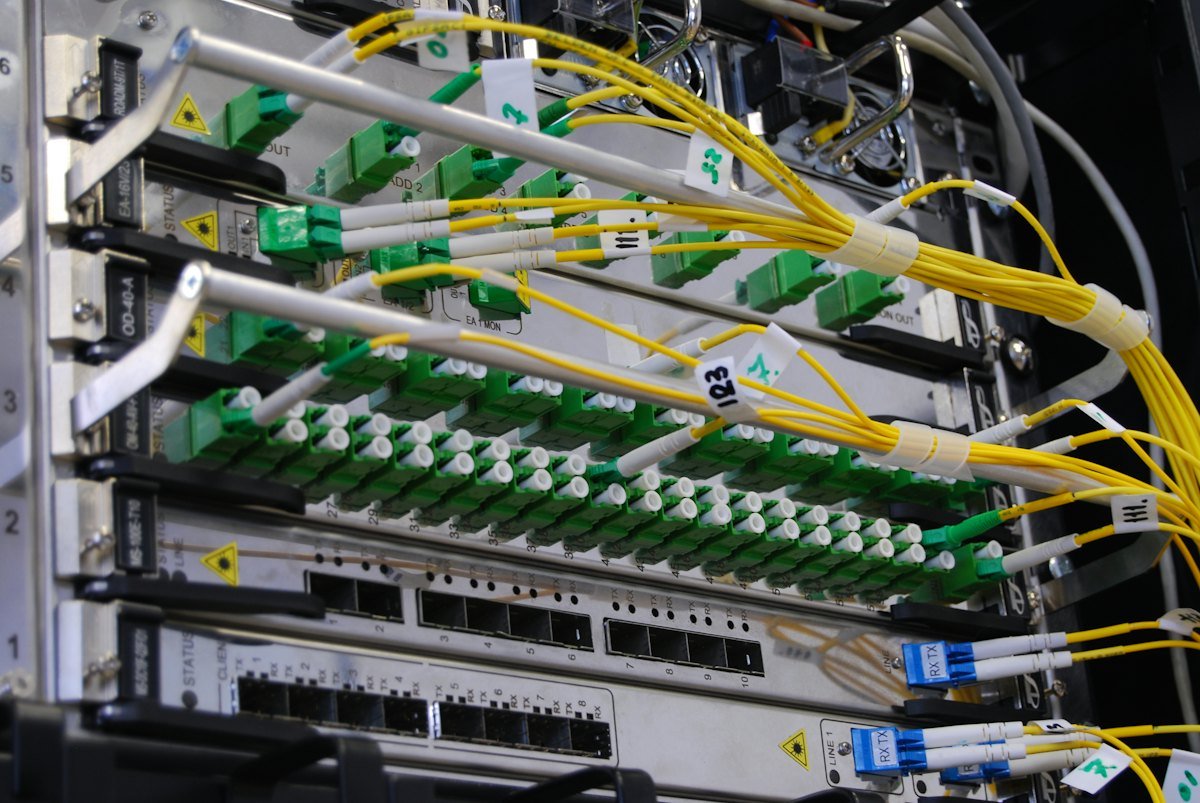
Network design used to be about making everything inside the office able to reach everything else, with a firewall at the edge. That model assumed the inside could be trusted. With staff working remotely, applications in the cloud and attackers routinely getting a foothold through phishing, the inside can't be trusted any more.
Zero trust, in plain terms
NIST's Special Publication 800-207, published in August 2020, defines zero trust architecture. Its core idea is that no user or device gets automatic trust because of where it sits on the network, inside the office or on the internet, or because the company owns the device. Users and devices are checked before each session with a company resource, and protection focuses on resources such as applications, data and accounts rather than network segments.
Zero trust is a direction, not a product. For a mid-size company, it shows up as a few concrete design choices.
The design principles that matter
Segment the network
Separate networks by purpose: staff devices, servers, guest Wi-Fi, printers and building systems, and anything you can't patch, such as old industrial equipment. Control traffic between segments with firewall rules that allow only what is needed. Segmentation is what stops ransomware on one laptop from reaching the backup server.
Build in redundancy where downtime is expensive
Give critical sites two internet links from different providers, ideally entering the building by different routes. Use redundant core switches and firewalls in pairs. Make sure power to network equipment is on a UPS.
Put access control in front of applications
Replace broad VPN access with per-application access tied to identity and device health. Users get to the applications they need, not to the whole network.
Manage centrally and keep it documented
Keep an up-to-date network diagram, an IP address plan and a record of firewall rules with a reason for each. Configuration backups for every switch, router and firewall make recovery from a failure a matter of minutes.
Monitor it
Collect logs from firewalls, VPNs and network devices, and alert on unusual traffic between segments.
Where to start
Most mid-size networks didn't start with these principles in mind. Pick the biggest risk first, which is usually a flat network where every device can reach every server, and segment it in stages, starting with servers and backups.
What IT teams should do
- Draw the current network and mark which segments can reach your servers and backups.
- Separate guest Wi-Fi, printers and unmanaged devices from staff and server networks.
- Check that critical sites have two independent internet links.
- Back up the configuration of every network device and test a restore.